Clarified recipient handling on the send email endpoint. The email field may contain multiple addresses separated by ; or ,, and each address is now validated independently against the organization / verified-domain permission rule. Addresses that do not meet the rule are dropped and the email is sent only to the permitted recipients (the response message lists any dropped recipients); if no address meets the rule the request fails with a 400 Bad Request.
HackerOne API Changelog hackerone.com
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
 Australia news LIVE: PM meets Trump, Modi and Takaichi at Quad meeting in Manila; Australia imposes fresh sanctions targeting illegal Israeli settlements, human rights abuses against Palestinians
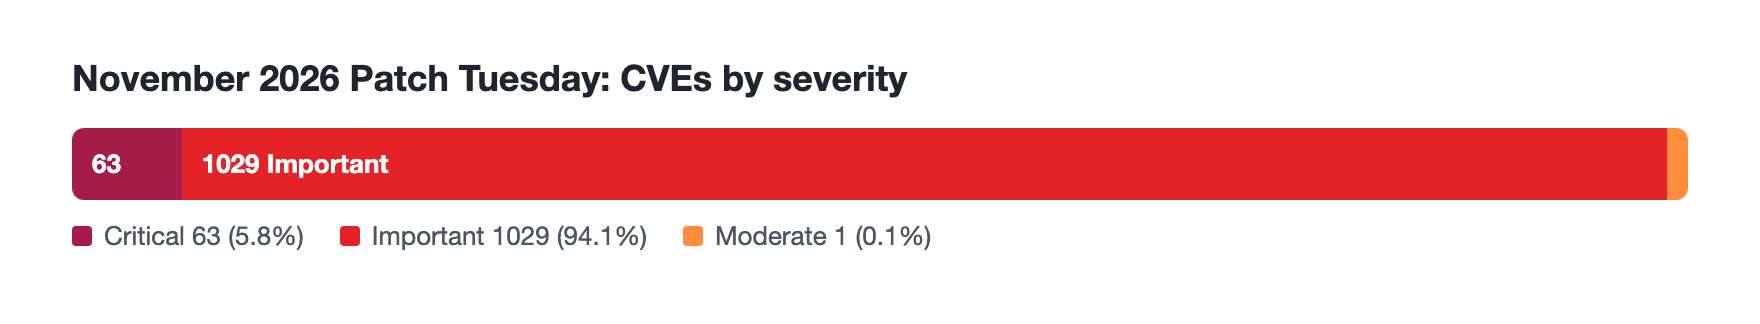 Microsoft’s November 2026 Patch Tuesday addresses 1093 CVEs (CVE-2026-124194)
 How to contain shadow AI, as it takes on multiple forms and spreads throughout your environment